All business manuals · Download PDF manual and fillable forms
AIT Technology · Practical implementation manual
Using AI in cybersecurity: a controlled operating manual
Use AI to assist alert triage, investigate evidence and improve security operations while keeping data, permissions and response decisions under control.
Version 1.0 · Published and sources checked
For: Security/IT leads, managed service owners and managers considering AI-assisted defensive workflows.
The process at a glance
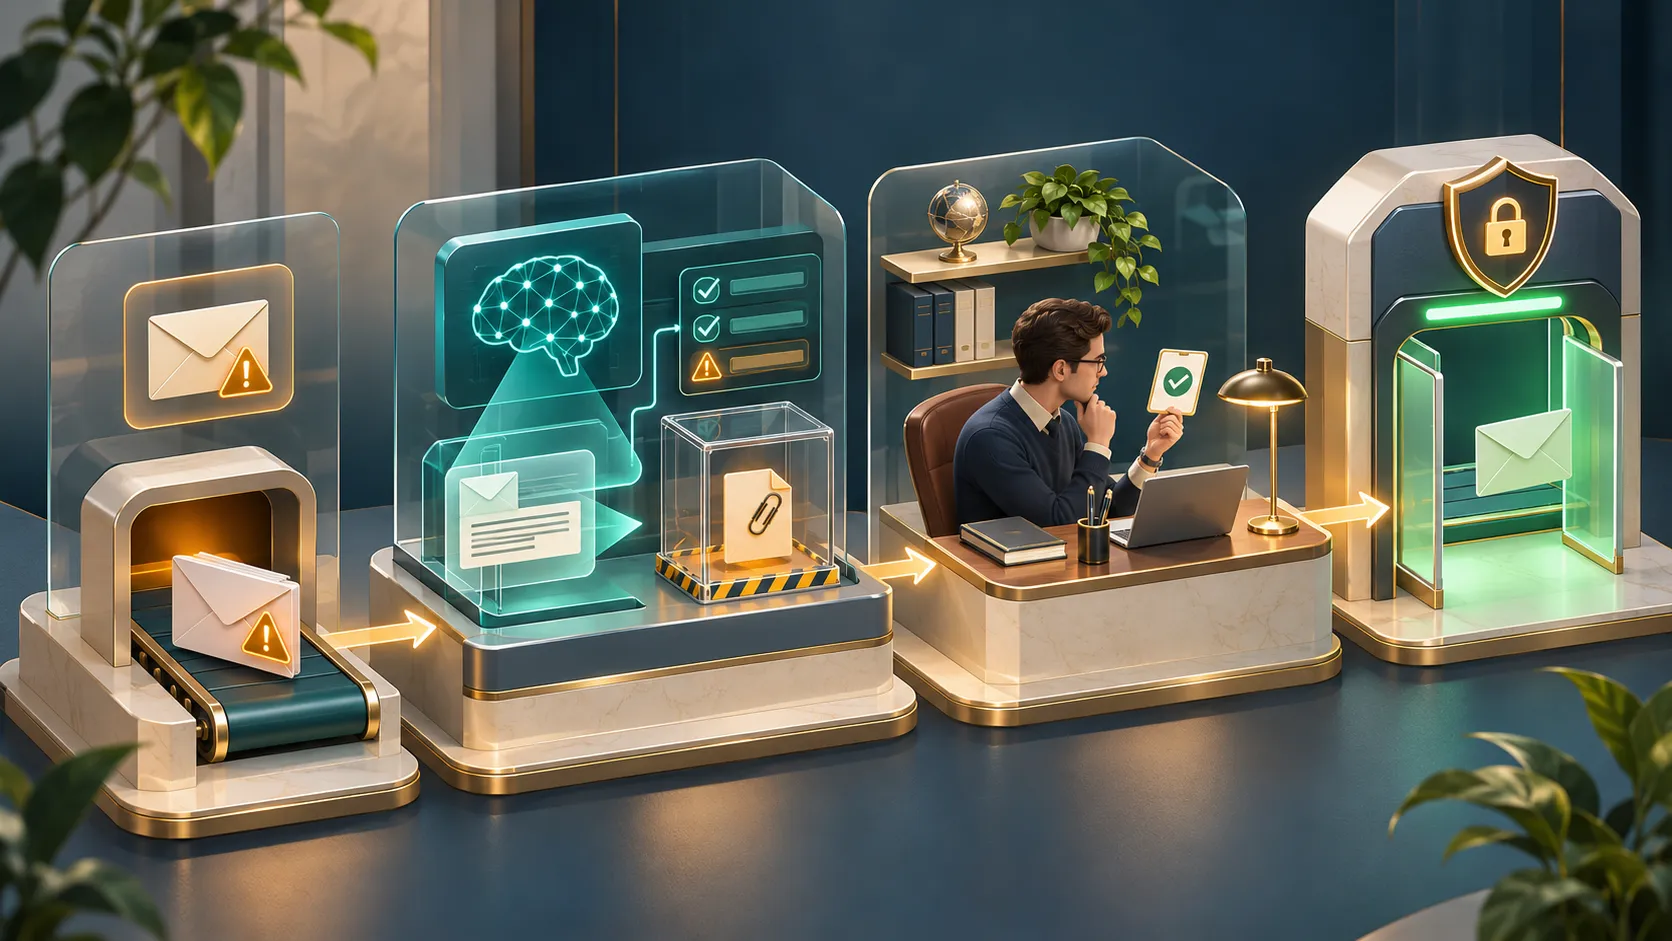
Use these stages as a visual route through the work. Detailed actions, decision owners and exit checks follow in the procedures.
- Receive untrusted evidence
- Minimise and validate
- AI-assisted analysis
- Human decision
- Controlled action and audit
A handoff requires a named owner and a recorded result. If a safety, data-access or approval condition is not met, pause the affected action and escalate.
Operating framework
1. Use AI as an assistant to a defined defensive task
Useful candidates include summarising alerts, grouping related cases, drafting incident timelines, searching approved playbooks and explaining log fields to an analyst. These are potential uses to evaluate, not claims that a model will reliably detect attacks. Compare with existing rules and analyst practice.
AI should not independently decide that an account is safe, close a serious incident or authorise destructive response. Begin in read-only shadow mode. Keep conventional detection, backups and access controls active. AIT Technology can design a bespoke integration and review workflow around the tools you already use; licensing, coverage and response hours are agreed separately.
2. Treat attacker-controlled content as hostile input
An email, attachment, web page, support ticket or log field can contain instructions aimed at the model. An attacker may ask it to ignore policy, disclose secrets, mark an alert harmless or call a tool. The appearance of an instruction inside evidence does not grant it authority.
Keep evidence separate from trusted instructions and mark its origin. Restrict input types and size, minimise data and prevent automatic retrieval of arbitrary URLs or internal destinations. Use an authorised isolated analysis environment for suspicious attachments. A prompt saying “ignore malicious instructions” is useful guidance but cannot guarantee protection.
3. Put enforcement outside the model
The model receives only the evidence it needs and no credentials for broad security administration. A separate tool gateway validates action type, target, reviewer approval, rate limits and expiry. Keep default-deny permissions and a central stop control. Do not let generated text become a shell command, firewall rule or SQL statement without independent validation.
High-impact actions such as disabling users, isolating production devices, deleting messages, blocking network ranges or rotating shared secrets need the authorised response process and relevant business/safety review. A model recommendation is not an approval. Keep a reversible action and recovery path wherever practical.
4. Require traceable claims and measure failures
Ask for observed facts, source event references, uncertainty and suggested next checks in separate fields. An analyst should be able to trace a claim to an original event. A numerical confidence score generated by a model is not a calibrated probability of compromise. Missing logs must be reported as missing, not interpreted as no attack.
Evaluate benign and malicious samples, false positives, missed cases, cross-case information leakage and prompt-injection attempts. Measure analyst review time and factual accuracy. Retest after model, prompt, detection-source or action-tool changes. A successful demo on one phishing email does not establish detection effectiveness.
5. Protect security data and retain useful evidence
Security records can reveal personal data, secrets, business structure and attacker activity. Use an approved account/service, minimised inputs, appropriate retention and access controls. Redact credentials with a tested process; do not assume that asking the model to remove secrets prevents them reaching the provider.
Preserve original evidence in the approved evidence store and link derived summaries to it. Record collection time, source, transformations and access where required. AI summaries are working notes, not forensic proof. Specialist investigations may require additional evidence-handling controls and qualified support.
6. Introduce autonomy in explicit stages
Stage 1: read-only analysis on synthetic/historical authorised data. Stage 2: shadow analysis of approved live data, with no actions. Stage 3: analyst-approved bounded actions through a separate executor. Consider any further automation only after measured evidence, risk assessment and specific approval; do not infer it from a general wish for efficiency.
Keep fallback playbooks usable without AI. Pause the AI component on boundary failures, unexplained action, unsafe output or cost limits while preserving essential security monitoring. The response owner decides when to resume after a documented fix and retest.
Department responsibilities
Assign actual names and deputies to these roles. Combining roles in a small company does not remove accountability or the need for review.
| Department / owner | Routine | Escalate when | Keep a record |
|---|---|---|---|
| Security / ITSecurity operations owner | Review AI summaries against original events; maintain detection and tool boundaries. | Injected instructions, fabricated evidence or unauthorised action. | Case references, reviewer decisions and action receipts. |
| Business operationsService / site owner | Define the impact and safe window for containment actions. | Proposed action could interrupt production or safety-critical work. | Containment and restart approvals. |
| Privacy and legalDesignated privacy lead | Approve categories of logs/messages and processing arrangements. | Sensitive evidence sent to an unapproved service or possible disclosure. | Assessment, retention and reporting decisions. |
| HR and staff supportHR / support lead | Provide a clear reporting route and avoid treating model allegations as facts about staff. | A person may be wrongly accused or a personnel decision proposed. | Human investigation and appropriate restricted case notes. |
| Leadership and suppliersRisk owner / service manager | Approve scope, spend, coverage and supplier responsibilities. | No competent reviewer, service outage or proposal for wider autonomy. | Service scope, acceptance evidence and authority matrix. |
Adapt the manual to your type of business
These are planning scenarios, not assessments of particular organisations. Add sector-specific duties, contractual requirements and safety expertise before adoption.
Office / professional services
Protect or improve: Mailbox and identity alert triage.
Example scenario: A malicious email asks the assistant to label itself safe.
Tailor the process: Use read-only message access, preserve headers and require analyst verification of identity events.
Retail / e-commerce
Protect or improve: Website, admin and account anomalies.
Example scenario: A model recommends blocking a large legitimate customer network.
Tailor the process: Check transaction/context evidence, use narrow temporary measures only with approval and verify rollback.
Manufacturing / logistics
Protect or improve: Detection without disrupting physical operations.
Example scenario: An isolation recommendation affects an operational controller.
Tailor the process: Exclude uncontrolled OT actions; coordinate with engineers and safety owners using a tested incident plan.
Care / education / charities
Protect or improve: Protect sensitive user and beneficiary information.
Example scenario: An alert includes confidential case content.
Tailor the process: Minimise input, enforce access and retention, and involve the relevant privacy/safeguarding leads.
Software / managed services
Protect or improve: Tenant isolation, secrets and security-tool integrations.
Example scenario: An assistant mixes evidence or executes an action across customers.
Tailor the process: Enforce tenant boundary in storage, retrieval and execution; test it independently of model instructions.
Step-by-step procedures
Use only within the approved company scope. Timescales, technical commands, contact details and escalation authority must be completed for your environment. The completion check is an evidence requirement, not a tick-box guarantee.
Procedure 01
AI-assisted suspicious-email triage
- Accountable owner
- Security analyst
- Start when
- Reported suspicious message.
- Collect the minimum approved metadata and text without opening an attachment on an ordinary workstation.
- Label content untrusted; disable model action tools and arbitrary URL retrieval.
- Request observed indicators, uncertainty and evidence references; do not ask only “safe or unsafe?”.
- Analyst checks sender/authentication context and relevant identity/security events using approved tools.
- Record a human disposition and trigger conventional response when indicated.
Evidence: Original message reference, derived summary, analyst checks and decision.
Completion / handoff: Disposition has traceable evidence; model output alone cannot close the case.
Procedure 02
AI-assisted alert correlation
- Accountable owner
- Security operations lead
- Start when
- Multiple related security alerts.
- Limit input to the authorised tenant/case and relevant time window.
- Ask the model to group observations and cite original event IDs.
- Validate the timeline, time zones, identities and gaps.
- Check alternative explanations and missing sources.
- Escalate according to impact and the normal incident plan, not a model confidence number.
Evidence: Event references, checked timeline and escalation rationale.
Completion / handoff: Analyst accepts the correlation with uncertainty recorded.
Procedure 03
Approve a response action
- Accountable owner
- Authorised incident lead + business owner where needed
- Start when
- AI suggests account/device/network containment.
- Verify target identity, supporting evidence and business impact independently.
- Choose the narrowest approved action with expiry/rollback.
- Record explicit approval outside the model output.
- Executor checks permission, target, approval and limits; return an actual receipt.
- Verify the effect and monitor for unintended disruption.
Evidence: Approval, executor receipt and post-action test.
Completion / handoff: Authorised action verified or reversed; uncertain execution reconciled.
Procedure 04
Prompt-injection attempt
- Accountable owner
- Security lead + AI service owner
- Start when
- Evidence tries to redirect instructions, reveal secrets or invoke tools.
- Do not follow the embedded commands; preserve a minimal restricted example.
- Pause action-capable processing for the affected route if a boundary may have failed.
- Check whether any data was disclosed or tool action occurred; use the incident process when needed.
- Fix input, retrieval or executor boundaries, not only wording.
- Retest with the original and varied adversarial examples before owner-approved resume.
Evidence: Attack sample reference, actual tool/data effects and regression tests.
Completion / handoff: Boundary holds in relevant tests and affected data/actions are assessed.
Procedure 05
Incorrect AI incident summary
- Accountable owner
- Incident lead
- Start when
- Summary invents facts, omits impact or assigns blame.
- Mark the draft unverified and stop onward distribution.
- Compare each material claim with original evidence.
- Correct the timeline and affected scope; separate assumptions.
- Review any decisions already based on the incorrect summary.
- Update the evaluation set and review process.
Evidence: Corrected version, source references and decision review.
Completion / handoff: Approved human account replaces the draft and affected decisions are addressed.
Procedure 06
Disable the AI component safely
- Accountable owner
- AI/security service owner
- Start when
- Boundary failure, unexpected spend, unsafe behaviour or provider outage.
- Disable model jobs/action access at the independent controller.
- Keep conventional security monitoring and incident channels running.
- Preserve approved logs and queued evidence without uncontrolled retries.
- Assign human handling for urgent cases and evaluate the failure.
- Require an authorised restart after the relevant tests and budget/security checks.
Evidence: Stop confirmation, fallback coverage and restart decision.
Completion / handoff: No further AI actions/spend beyond already in-flight bounded work; essential detection continues.
Records and templates to customise
Copy these field sets into your approved ticketing, document or workflow system. A record should have a named owner, access restrictions, retention and a review date. Store evidence by reference; do not paste secrets into forms.
AI use-case and data approval
Workflow / sponsor / process owner / data owner / approved service and account / permitted inputs / prohibited data and actions / affected people / privacy and security assessment / reviewer / baseline / pilot budget / stop conditions.
Evaluation and release record
Dataset and source authorisation / model, prompt and tool versions / expected answers / normal, edge and adversarial cases / acceptance thresholds / measured errors / review time / cost / access-boundary tests / release approver / fallback / review date.
Action approval and receipt
Case ID / evidence references / suggested action / exact target / business impact / independent validation / permitted executor / human approver / approval expiry / actual receipt / post-action verification / rollback.
AI incident and pause record
Detected time / version / unsafe or incorrect behaviour / affected data or decisions / actual tools invoked / stop confirmation / human fallback / evidence location / corrective action / retest / authorised restart.
Suggested incident prioritisation
- Urgent: ongoing compromise, suspected sensitive-data exposure, fraud, safety risk or loss of a critical process. Contact the named lead immediately through a trusted route.
- Significant: contained disruption or a material weakness requiring coordinated action. Assign an owner and agreed response deadline.
- Routine: low-impact issues and improvement requests. Track to closure and escalate if scope changes.
Define company response times and cover explicitly. This manual and AIT's contact form are not emergency response services.
AIT Technology can build a version that fits your company
We can work with you to map existing processes, tailor departmental procedures, configure agreed controls and create custom software or integrations where standard tools leave a gap. Potential deliverables include onboarding workflows, access-approval forms, incident registers, AI review queues, operational dashboards and controlled connections between existing systems.
- Discover: understand your business, departments, systems and risks.
- Design: agree scope, owners, information boundaries and acceptance tests.
- Implement: configure or build the agreed solution with controlled access and a rollback plan.
- Validate: test representative scenarios, train named users and hand over documentation.
- Maintain: agree ownership, review cadence and any support service separately.
We confirm suitability, specialist needs, licence costs and delivery scope before commitments. No universal price, compliance certification, 24/7 coverage or guaranteed business result is implied.
Talk about your company's requirementsSources, limitations and maintenance
This is original AIT implementation guidance informed by the public sources below, checked 18 November 2026. The role assignments, templates, frequencies and sample workflows are proposed operational designs to customise; they are not verbatim official requirements. Linked guidance may change. Review the company version after incidents, service/model changes, new legal obligations and at its agreed review date.
- NCSC: guidelines for secure AI system development
- NCSC: incident management
- ICO: guidance on AI and data protection
- NCSC: secure AI development — further guidance
Regulated, safety-critical, clinical, payment and consequential decisions require appropriate specialist assessment. A general manual does not replace that work.
Explore the other business manuals · Read our latest articles
Download your ready-to-use pack
Branded covers, company footer and interactive forms. Use a PDF reader supporting AcroForms, save locally and reopen to check your entries. Browser support varies. The files do not send completed records to AIT.