All business manuals · Download PDF manual and fillable forms
AIT Technology · Practical implementation manual
AI implementation manual for business teams
Select useful workflows, protect information, test results and deploy controlled AI with named owners. Adapt the process to your departments and existing systems.
Version 1.0 · Published and sources checked
For: Business owners, process owners, IT, data/privacy leads and staff using or building AI-supported workflows.
The process at a glance
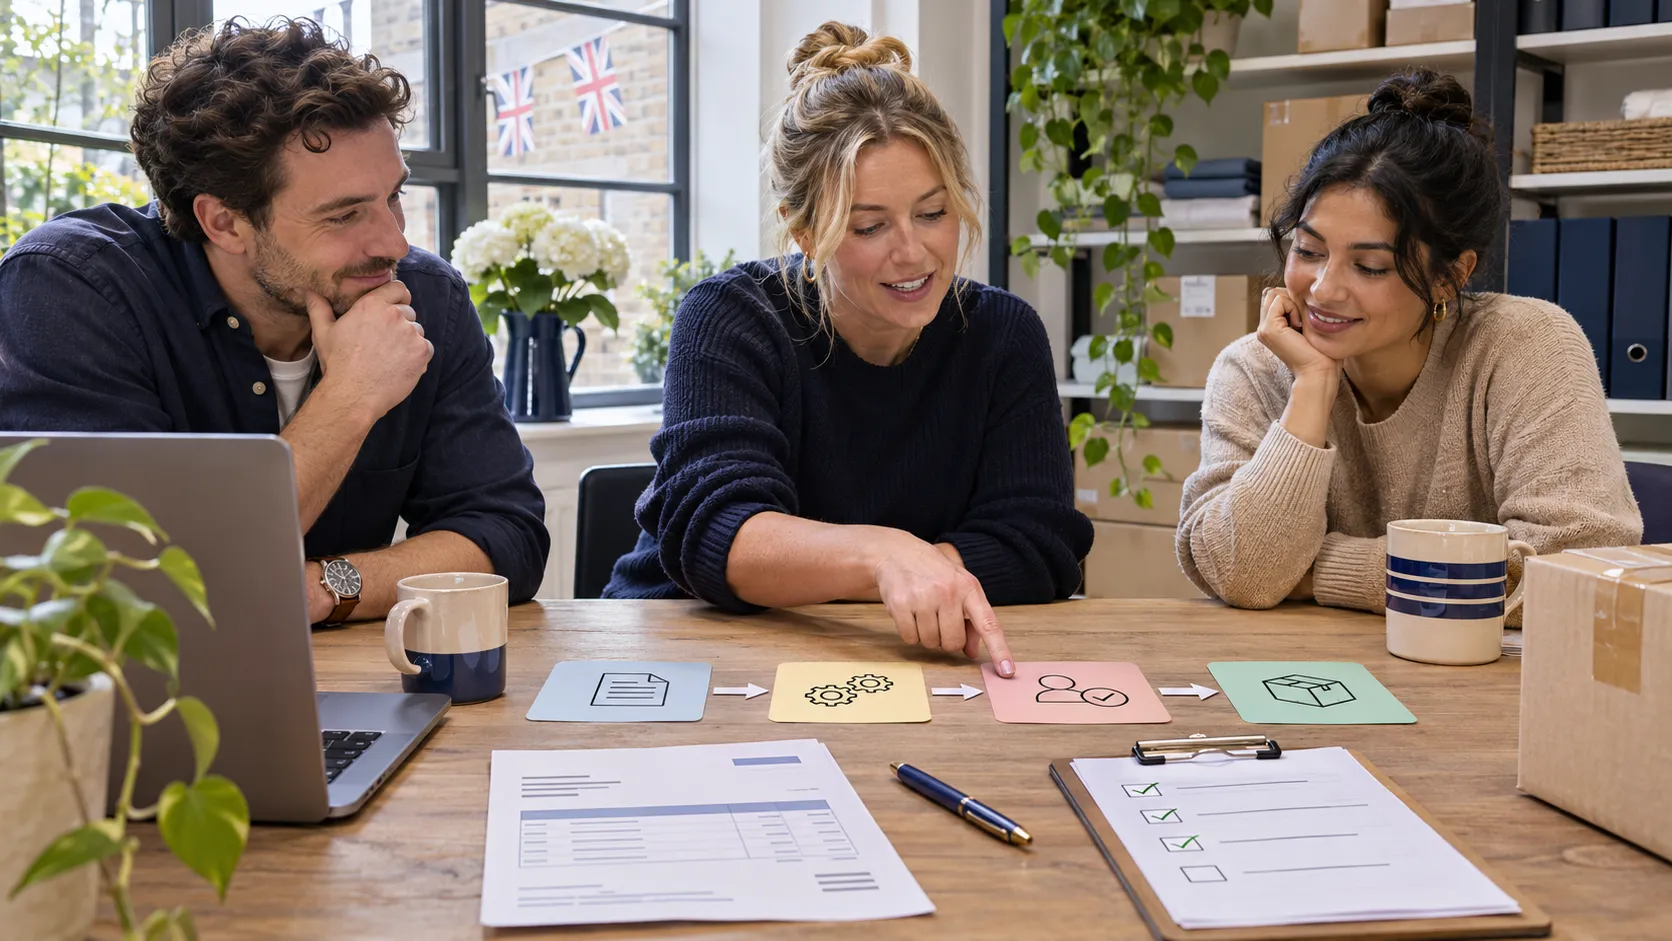
Use these stages as a visual route through the work. Detailed actions, decision owners and exit checks follow in the procedures.
- Choose one workflow
- Approve data and access
- Build a bounded pilot
- Test with people
- Release, measure and improve
A handoff requires a named owner and a recorded result. If a safety, data-access or approval condition is not met, pause the affected action and escalate.
Operating framework
1. Start with a business outcome
Choose one repeated task with a clear input, output and reviewer. Record the current time, errors, rework and cost before changing it. Examples include drafting responses, extracting document fields or searching approved procedures. A process should not be automated solely because a model can produce a convincing demonstration.
AIT Technology can customise this manual and create bespoke AI applications, integrations, approval flows and dashboards around your company. We can help connect an agreed workflow to existing tools without assuming every system has a suitable API. Discovery establishes feasibility, data access, licence needs, acceptance tests and support scope.
2. Assign accountable roles and define boundaries
The business sponsor owns value and risk. The process owner defines the workflow and signs off results. The data owner authorises the information used. IT controls identity, integrations and operation. A reviewer checks outputs. The privacy/security lead reviews sensitive data and potential harm. One release owner can pause or roll back the system.
Define permitted inputs, outputs, users and external actions. Distinguish drafting from sending, recommending from approving and searching from modifying records. Keep money movement, employment decisions, health/safety decisions and other high-impact actions outside an unsupervised pilot. Obtain relevant specialist assessment before expanding scope.
3. Approve services and information handling
Maintain an AI service register: account type, owner, contract, purpose, permitted data, retention, processing locations, access, subprocessors, export/deletion and integration permissions. Check the current configuration and terms, not a general claim that a product is “private”. Keep secrets out of prompts and logs.
Begin with fictional or suitably de-identified samples. De-identification itself requires assessment; removing a name may not make data anonymous. Where personal data is involved, assess lawful use, transparency, minimisation, retention and whether a data protection impact assessment is required. ICO guidance is a starting point; review the current position for the actual use case.
Microsoft documents enterprise protections for eligible Copilot Chat experiences, including specific handling of prompts, responses, uploads and web search. These are product/account-specific commitments, not a blanket statement about every chatbot or connected tool. Verify the approved tenant, feature and data route before using real business information.
4. Build a controlled and testable workflow
Write the task specification: approved source, expected fields, output format, missing-value behaviour, evidence links and escalation conditions. Use deterministic checks for totals, required fields and permitted destinations. Prompt instructions help shape behaviour but cannot replace access controls or validation.
Treat uploaded documents, web pages, email and retrieved passages as untrusted data. Separate them from controlling instructions. Give tools the smallest necessary permissions; use a restricted integration layer that validates actions and approvals independently of the model. Never give a draft generator authority to grant itself access or change its spending limit.
Define per-job call, token, time, retry and spend limits. Stop on repeated failure; maintain a queue/dead-letter route for human review. A timeout should not trigger an uncontrolled retry that sends the same message or creates the same order twice. Use idempotency and reconcile uncertain outcomes.
5. Evaluate before production
Build a representative, authorised test set including normal cases, missing fields, conflicting data, unusual layouts and malicious instructions. Keep a held-out set for release checks. Compare the reviewed result with the existing process; measure correction time and errors as well as generation speed.
Set acceptance thresholds before examining results. For an invoice extractor, test exact field accuracy and route uncertain or inconsistent records to a person. For an assistant, test whether it cites the right approved source and admits missing information. Do not publish invented benchmark results. Have the process owner approve release evidence.
6. Operate, review and improve
Release to a limited group with clear ownership, user guidance, a visible reporting route and an accessible non-AI fallback. Log model/configuration versions, actions, approvals, costs and failures with appropriate minimisation and retention. Protect logs because they may reveal confidential business information.
Review quality, incidents, cost per accepted output and actual time saved. Re-evaluate after model, prompt, source, permission or workflow changes. Pause when error thresholds, budget or security conditions fail. An apparent time saving that shifts unrecorded work to reviewers is not a verified improvement.
In the first 30 days, select a workflow and complete a synthetic pilot. By day 60, test approved representative data and controlled integrations. By day 90, assess a limited release against agreed quality and cost criteria. These are planning milestones to tailor, not guaranteed delivery dates.
Department responsibilities
Assign actual names and deputies to these roles. Combining roles in a small company does not remove accountability or the need for review.
| Department / owner | Routine | Escalate when | Keep a record |
|---|---|---|---|
| LeadershipSponsor / risk owner | Approve the business case, prohibited uses, budget and stop conditions. | Uncontrolled cost, harmful output, unclear ownership or proposed scope expansion. | Use-case register and release/risk decisions. |
| FinanceFinance process owner | Use AI for draft extraction/classification with deterministic checks and human approval. | Changed bank details, inconsistent totals or suggested payment actions. | Source reference, validation and payment approval outside AI. |
| HRHR + privacy lead | Draft general onboarding and policy explanations from approved material. | Sensitive employee data, ranking people or consequential employment recommendations. | Approved sources, review and fairness/privacy assessment where relevant. |
| Sales and marketingCommercial owner | Draft accurate copy and follow-up suggestions; verify price, product features and claims. | Invented benefits, unapproved outreach, misleading claims or disclosure of client material. | Reviewed draft, source facts and sending approval. |
| Customer serviceService owner | Prepare suggested answers from a controlled knowledge base. | Unanswered policy question, refund/contract commitment or vulnerable customer issue. | Evidence source, reviewer and actual response sent. |
| Operations and logisticsOperations lead | Draft instructions and identify exceptions without altering physical control systems. | Unsafe recommendation, wrong order/stock record or conflicting source data. | Validated exceptions and reconciliation with the system of record. |
| IT and developmentTechnical owner | Control model integrations, source access, secrets, evaluations, deployment and logs. | Prompt injection, leaked credentials, privilege escalation or repeated tool failure. | Versioned specification, test results, permissions and rollback record. |
| Privacy and legalDesignated assessment lead | Review data purpose, notices, contracts, retention and affected-person risks. | Unapproved personal-data use or consequential automated decisions. | Assessment, authorised data categories and agreed safeguards. |
Adapt the manual to your type of business
These are planning scenarios, not assessments of particular organisations. Add sector-specific duties, contractual requirements and safety expertise before adoption.
Retail / e-commerce
Protect or improve: Product descriptions, catalogue cleanup and draft customer responses.
Example scenario: An AI invents a product specification or refund promise.
Tailor the process: Ground in approved product/policy records; block unsupported claims and review before publication.
Manufacturing
Protect or improve: Document search, maintenance-note summaries and quality exception review.
Example scenario: An answer suggests an unsafe machine setting.
Tailor the process: Keep control/safety decisions with competent staff; use approved versioned documentation and prohibit autonomous machine commands.
Logistics / warehousing
Protect or improve: Document extraction, order exceptions and reporting.
Example scenario: An extraction assigns an order to the wrong customer.
Tailor the process: Validate identifiers and totals against the system of record; send conflicts to human review before import.
Professional services
Protect or improve: Drafting, matter search and document comparison.
Example scenario: A response mixes two clients’ information.
Tailor the process: Enforce project/client permissions in retrieval, not only in a prompt; use confidentiality review.
Care / health-related services
Protect or improve: Low-risk administration and approved information assistance.
Example scenario: A draft makes a clinical or care recommendation.
Tailor the process: Limit to agreed administrative scope; assess sensitive-data and safety requirements with qualified sector leads.
Construction / field services
Protect or improve: Job-note structure, quotation drafts and documentation search.
Example scenario: An outdated drawing drives the recommendation.
Tailor the process: Validate document revision and approval status; preserve engineer sign-off and site-specific safety processes.
Hospitality
Protect or improve: Draft guest communications and internal knowledge search.
Example scenario: An assistant promises an unavailable room or service.
Tailor the process: Check actual availability and policy through approved interfaces; prevent autonomous booking commitments during the pilot.
Education / charities
Protect or improve: General content drafts, grant-document organisation and internal FAQs.
Example scenario: Personal information about a learner or beneficiary enters an unapproved service.
Tailor the process: Define restricted categories and safeguarding escalation; use fictional samples before approved data handling.
Step-by-step procedures
Use only within the approved company scope. Timescales, technical commands, contact details and escalation authority must be completed for your environment. The completion check is an evidence requirement, not a tick-box guarantee.
Procedure 01
Approve a new AI use case
- Accountable owner
- Sponsor + process/data owners
- Start when
- A team proposes an AI workflow.
- Describe the problem and baseline; identify affected users and decisions.
- List data, services, tools, costs and risks; define prohibited actions.
- Review privacy/security and contract requirements; assess whether simpler automation is adequate.
- Set acceptance thresholds, pilot budget and stop conditions.
- Approve only the bounded pilot, with a named reviewer and fallback.
Evidence: Use-case record, assessment and approval.
Completion / handoff: Scope and success criteria agreed before access is granted.
Procedure 02
Run a document-extraction pilot
- Accountable owner
- Process owner + technical owner
- Start when
- Repeated documents need structured fields.
- Select authorised synthetic samples and define a schema with required fields.
- Require missing/uncertain values to be flagged; prohibit guessed facts.
- Validate identifiers, amounts and allowed categories deterministically.
- Compare to a verified answer set and measure correction time.
- Route failed validation to a person; no automatic accounting/payment entry in the initial pilot.
Evidence: Dataset version, exact-match errors, review effort and failure cases.
Completion / handoff: Owner accepts measured quality or rejects/revises the workflow.
Procedure 03
Release a knowledge assistant
- Accountable owner
- Knowledge owner + IT
- Start when
- Staff need answers from internal procedures.
- Choose current approved sources and their access restrictions.
- Enforce user permissions during retrieval; test cross-client and restricted-document isolation.
- Require source references and “not found” handling.
- Test conflicting/outdated pages and embedded malicious instructions.
- Release to a limited group with reporting, review and a fallback to the source owner.
Evidence: Source inventory, access tests and evaluated answers.
Completion / handoff: No demonstrated access-boundary failure and agreed quality threshold met.
Procedure 04
Connect an action tool
- Accountable owner
- Integration owner + business approver
- Start when
- AI is proposed to send, update or create something.
- Separate suggestion from execution; define exact allowed actions and destinations.
- Use least-privilege credentials outside the prompt/workspace.
- Validate schema, permissions, cost and human approval in the execution service.
- Test duplicates, timeout-after-success and malicious payloads using synthetic data.
- Enable only the authorised scope with audit and a tested disable switch.
Evidence: Permission matrix, tool tests, approvals and action receipts.
Completion / handoff: External effects match the approved request and uncertain outcomes are reconciled.
Procedure 05
Respond to unsafe or incorrect AI output
- Accountable owner
- User + process owner + IT
- Start when
- Invented fact, leaked information or harmful instruction.
- Do not act on or forward the output as fact.
- Record a minimal authorised example and version; restrict access to sensitive material.
- Pause the affected workflow if boundaries or significant harm are involved.
- Assess data exposure and use the incident process if needed.
- Correct root causes and rerun relevant evaluations before reactivation.
Evidence: Incident/defect record, impact and retest.
Completion / handoff: Owner authorises resume with documented evidence, not only a rewritten prompt.
Procedure 06
Control cost and model changes
- Accountable owner
- Service owner
- Start when
- Budget threshold, recurring failure or provider/model update.
- Measure calls, tokens, retries and accepted outputs per workflow.
- Enforce local per-job and cumulative limits independently of provider alerts.
- Pause queued paid execution at limits; retain data and logs.
- Evaluate the new version on a held-out set before promotion.
- Require the authorised owner to approve budget or scope increases.
Evidence: Cost ledger, evaluation comparison and change approval.
Completion / handoff: Approved budget and tested quality restored; no automatic limit bypass.
Records and templates to customise
Copy these field sets into your approved ticketing, document or workflow system. A record should have a named owner, access restrictions, retention and a review date. Store evidence by reference; do not paste secrets into forms.
AI use-case and data approval
Workflow / sponsor / process owner / data owner / approved service and account / permitted inputs / prohibited data and actions / affected people / privacy and security assessment / reviewer / baseline / pilot budget / stop conditions.
Evaluation and release record
Dataset and source authorisation / model, prompt and tool versions / expected answers / normal, edge and adversarial cases / acceptance thresholds / measured errors / review time / cost / access-boundary tests / release approver / fallback / review date.
Action approval and receipt
Case ID / evidence references / suggested action / exact target / business impact / independent validation / permitted executor / human approver / approval expiry / actual receipt / post-action verification / rollback.
AI incident and pause record
Detected time / version / unsafe or incorrect behaviour / affected data or decisions / actual tools invoked / stop confirmation / human fallback / evidence location / corrective action / retest / authorised restart.
Suggested incident prioritisation
- Urgent: ongoing compromise, suspected sensitive-data exposure, fraud, safety risk or loss of a critical process. Contact the named lead immediately through a trusted route.
- Significant: contained disruption or a material weakness requiring coordinated action. Assign an owner and agreed response deadline.
- Routine: low-impact issues and improvement requests. Track to closure and escalate if scope changes.
Define company response times and cover explicitly. This manual and AIT's contact form are not emergency response services.
AIT Technology can build a version that fits your company
We can work with you to map existing processes, tailor departmental procedures, configure agreed controls and create custom software or integrations where standard tools leave a gap. Potential deliverables include onboarding workflows, access-approval forms, incident registers, AI review queues, operational dashboards and controlled connections between existing systems.
- Discover: understand your business, departments, systems and risks.
- Design: agree scope, owners, information boundaries and acceptance tests.
- Implement: configure or build the agreed solution with controlled access and a rollback plan.
- Validate: test representative scenarios, train named users and hand over documentation.
- Maintain: agree ownership, review cadence and any support service separately.
We confirm suitability, specialist needs, licence costs and delivery scope before commitments. No universal price, compliance certification, 24/7 coverage or guaranteed business result is implied.
Talk about your company's requirementsSources, limitations and maintenance
This is original AIT implementation guidance informed by the public sources below, checked 18 November 2026. The role assignments, templates, frequencies and sample workflows are proposed operational designs to customise; they are not verbatim official requirements. Linked guidance may change. Review the company version after incidents, service/model changes, new legal obligations and at its agreed review date.
- NCSC: guidelines for secure AI system development
- ICO: guidance on AI and data protection
- Microsoft: Copilot Chat privacy and protections
Regulated, safety-critical, clinical, payment and consequential decisions require appropriate specialist assessment. A general manual does not replace that work.
Explore the other business manuals · Read our latest articles
Download your ready-to-use pack
Branded covers, company footer and interactive forms. Use a PDF reader supporting AcroForms, save locally and reopen to check your entries. Browser support varies. The files do not send completed records to AIT.